
A bit over a month ago, we talked about the significant security issue that was exploited by security researchers to take control of a Jeep Cherokee from the driver from afar. The automotive and security world were scandalized that a hack of this magnitude with the potential for driver injury could occur. Chrysler has now issued a patch for the 2014 Jeep Cherokee that plugs the security hole that allowed hackers to take over the transmission and brakes of the car.
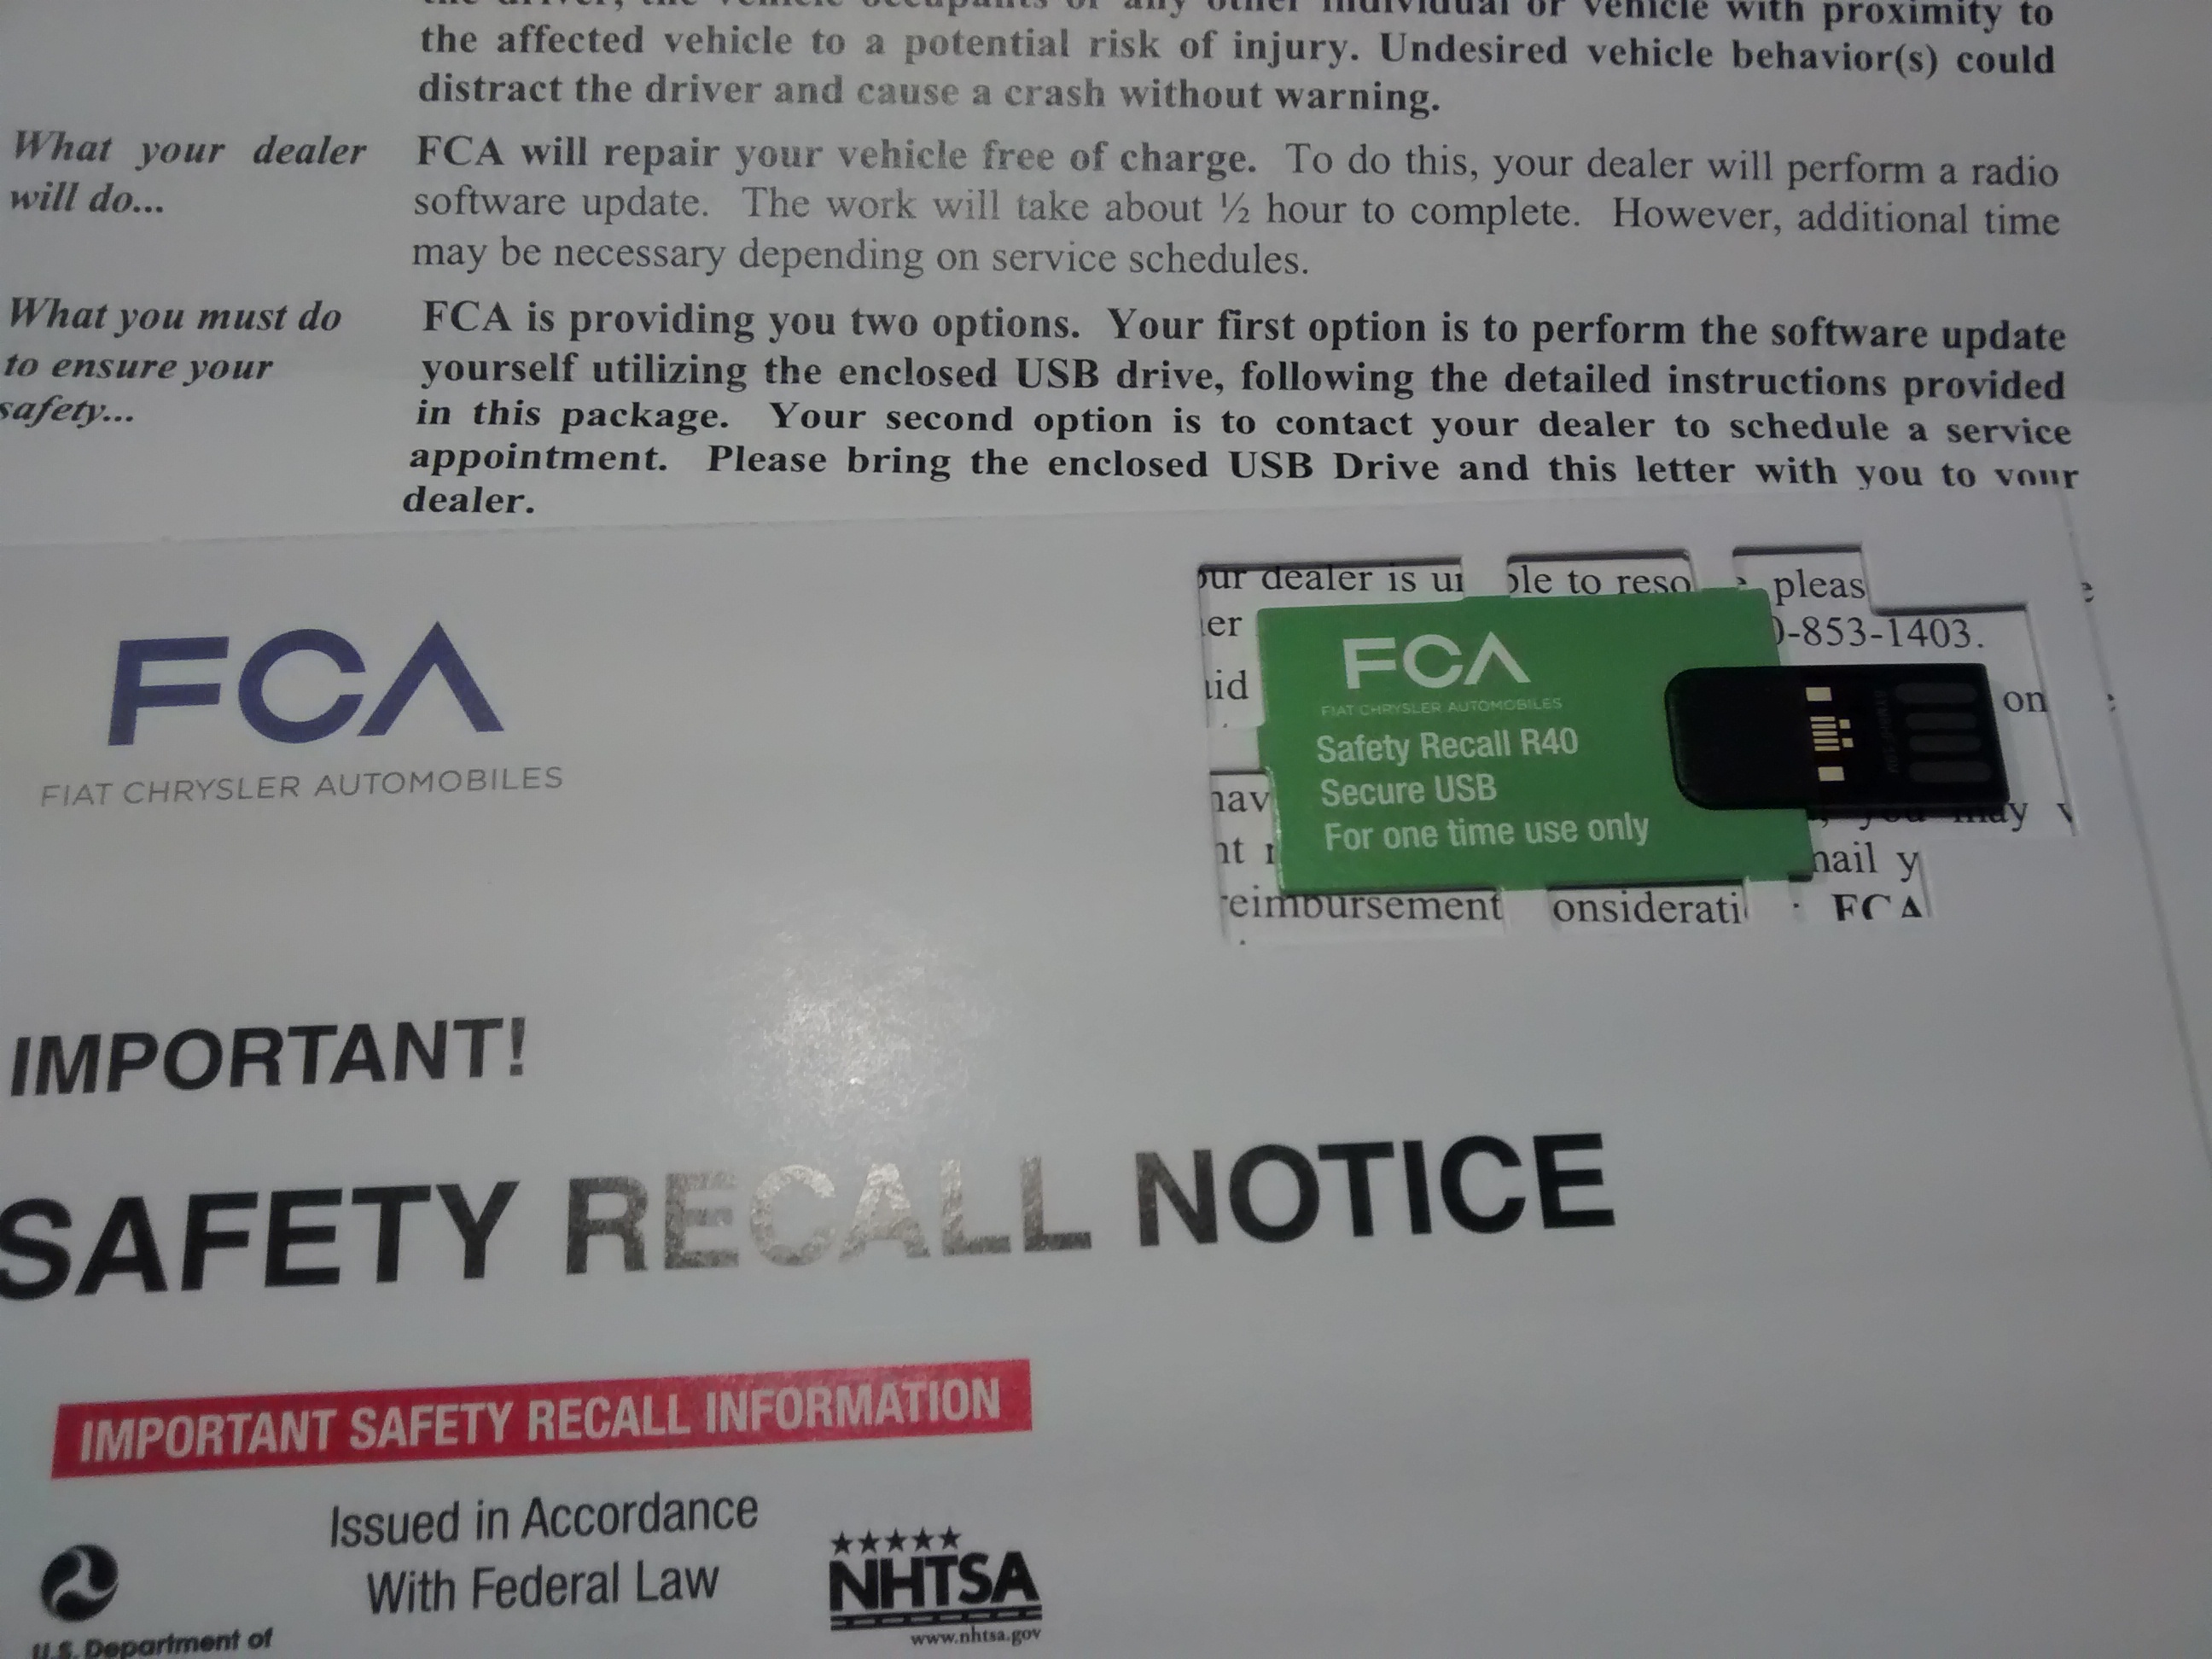
The patch was mailed to owners of the vehicle via the US Postal Service Inside a letter on a USB drive. The anger from some comes in that with this major security issue being patched this way, it opens the door for owners of these vehicles to be hacked in the future by spoofed similar mailers.

Chrysler says that the scenario of a spoofed mailer being sent out to trick vehicle owners into installing rouge software in their vehicles is only speculation. The automaker also pointed out that its drives are read only, which does nothing for the conditioning that the company has done to get drivers to plug flash drives received via the mail into their car when they look official.
The software patch sent out via USB isn’t the only way that cars are being protected from similar attack vectors in the future. Chrysler also added a layer of security on the Uconnect Sprint network connection to block wireless attacks like the one that took over some controls in the 2014 Cherokee.
(slashgear.com)


